// hosting explained
Egress firewalls, environment variables and read-only files: WordPress hardening, explained
Most WordPress security advice is about keeping attackers out. These three settings limit what an attacker can do if they get in.
KEY TAKEAWAYS
- Egress firewall: controls which outside servers your site can connect to, so malware can't easily phone home.
- Environment variables: keep API keys out of files a hacked plugin could read.
- Read-only filesystem: stops PHP writing files while you clean up a hacked site.
Egress firewall
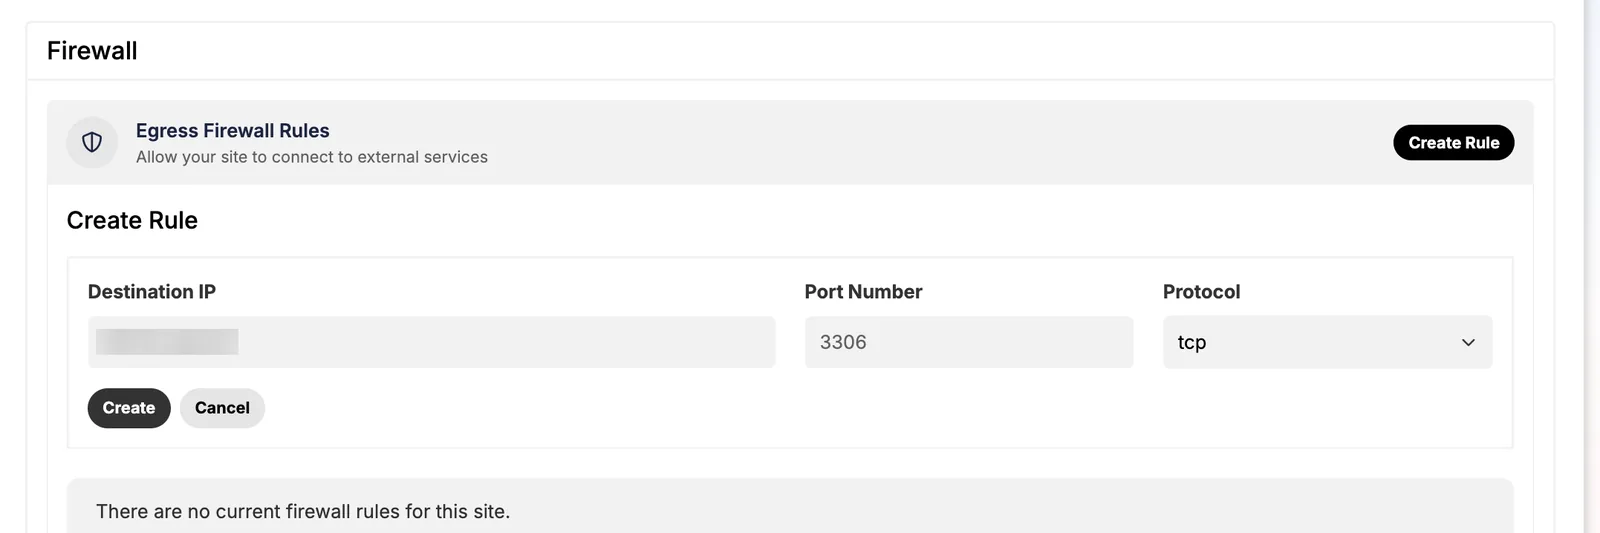
Normal firewalls filter incoming traffic. An egress firewall filters outgoing connections: you allow a destination IP, port and protocol your site legitimately needs, such as an external database on port 3306.
Environment variables for secrets
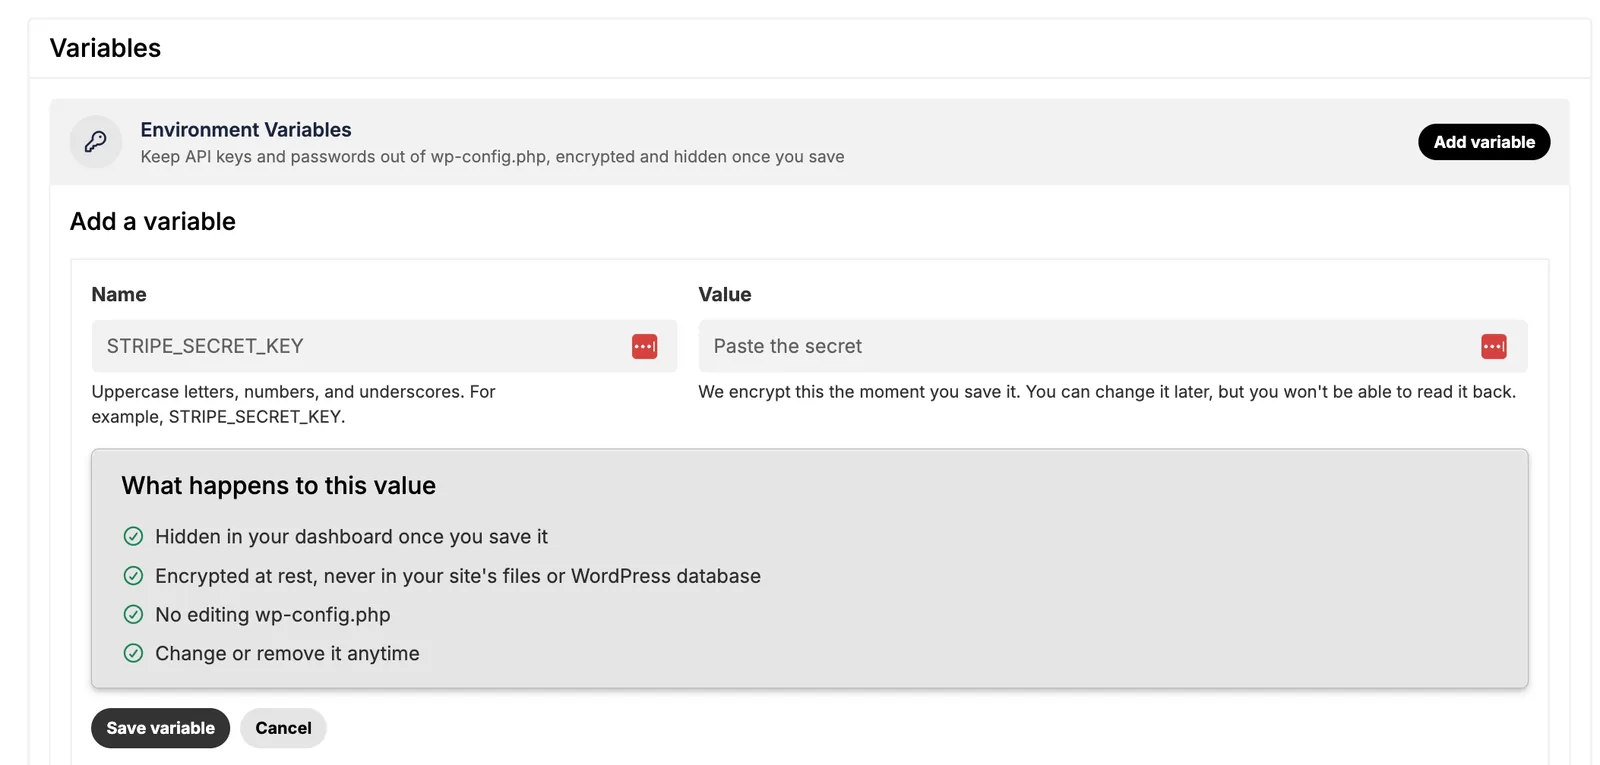
Put keys like STRIPE_SECRET_KEY in encrypted environment variables instead of wp-config.php. On Pressable they're encrypted at rest, hidden once saved and read in PHP with a helper class.
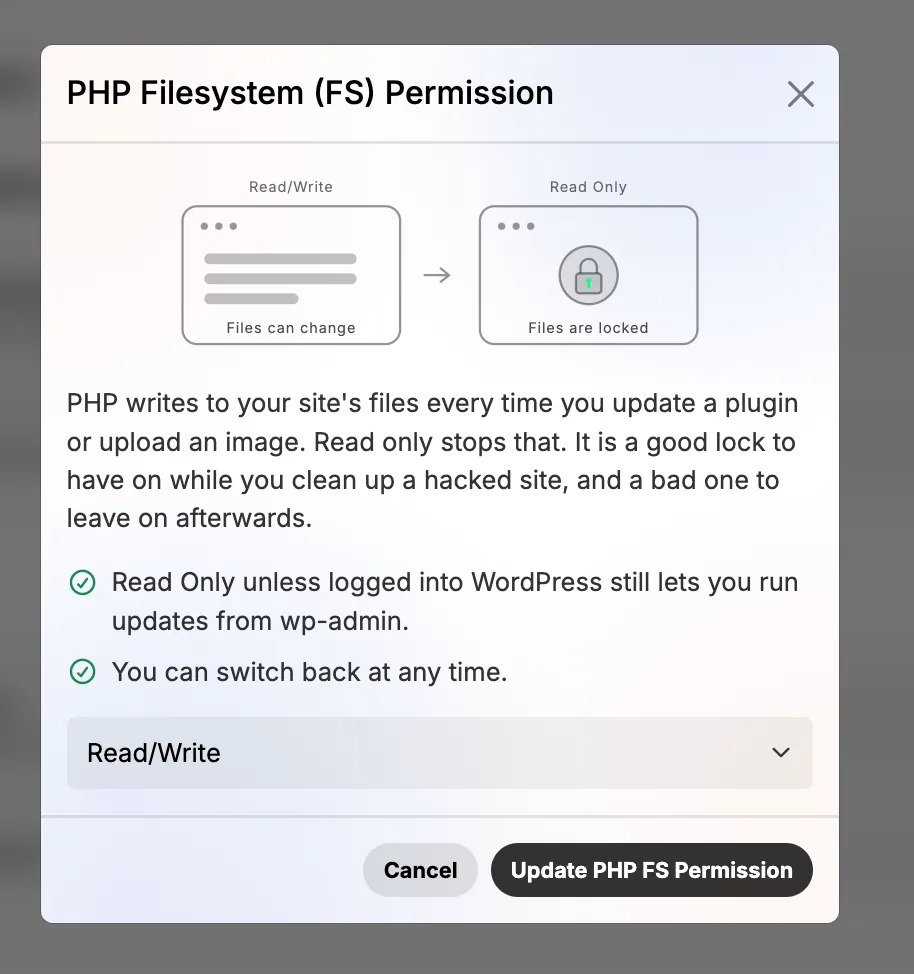
Read-only filesystem
PHP normally writes files when you update plugins or upload images. Switching to read-only stops that, which is ideal while removing malware. Pressable's "read only unless logged in" mode still lets you update from wp-admin. Switch it back after cleanup.